How to Better Secure Your Microsoft 365 Environment
Security experts offer Microsoft 365 security guidance as more attackers target enterprise cloud environments.
Source: darkreading.com
Stay updated with breaking news from Staff Editor. Get real-time updates on events, politics, business, and more. Visit us for reliable news and exclusive interviews.
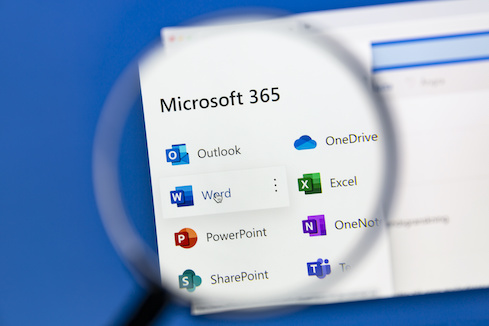
Security experts offer Microsoft 365 security guidance as more attackers target enterprise cloud environments.
Learn SAML: The Language You Don't Know You're Already Speaking Security Assertion Markup Language, a protocol most people use daily to log into applications, makes authentication easier for both admins and users. Here's what you need to know about SAML (and what it has to do with "GoldenSAML"). Security Assertion Markup Language (SAML): You may have heard of it. You've likely used it at least once today to log into a website portal or enterprise application. But what is SAML? How does it work? And why do you need to know about it? (Source: Mykyta via Adobe Stock) What Is SAML?
In a statement published Jan. 22, SonicWall officials wrote they detected an attack "by highly sophisticated threat actors exploiting probably zero-day vulnerabilities on certain SonicWall secure remote access products." As of Jan. 23, the company has confirmed its SonicWall Firewalls, NetExtender VPN Client, Secure Mobile Access (SMA) 1000 Series, and SonicWave Access Points were not affected in the recent attack. The SMA 100 Series, used to provide employees with remote access to internal resources, is under investigation but "may be used safely in common deployment use cases." Current ...

Attackers Leave Stolen Credentials Searchable on Google Operators behind a global phishing campaign inadvertently left thousands of stolen credentials accessible via Google Search. The attackers behind a summer 2020 phishing campaign accidentally exposed the credentials they stole to the public Internet, where they could be discovered with a simple Google search. Related Content: Last August, the operators launched a campaign with malicious emails disguised as Xerox scan notifications, Check Point researchers report in an analysis conducted alongside industrial cybersecurity firm Otorio. ...
Researchers with Recorded Future's Insikt Group collected more than 10,000 unique C2 servers across at least 80 malware families last year. Cobalt Strike accounted for 1,441 of the C2 servers and Metasploit made up 1,122; combined, they made up 25% of the total C2 servers. Detections of unaltered Cobalt Strike deployments represented 13.5% of C2 servers identified. Offensive security tools, also known as penetration testing tools and red teaming tools, have become part of attackers' toolkits in recent years. Some of these tools mimic an attackers' activity, and attack groups noticed an oppo...