'MountLocker' Ransomware Adds to Affiliate Extortion Racket
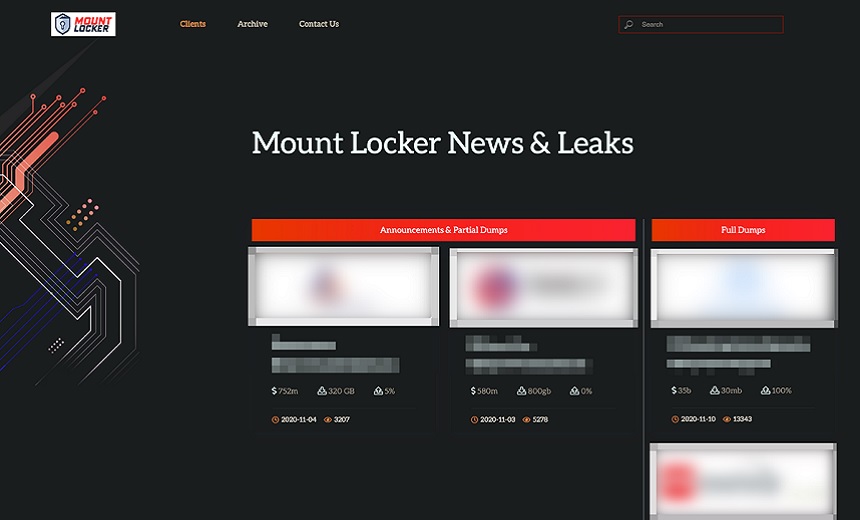
MountLocker's "News & Leaks" site hosted on the darknet (Source: BlackBerry) BlackBerry researchers are tracking a relatively new ransomware variant called MountLocker and the operators behind it, who are using affiliate cybercriminal gangs to help spread the malware, exfiltrate data and extort victims, sometimes for millions of dollars. The ransomware was first spotted by BlackBerry's Incident Response Team in July, and its code was updated in November to allow MountLocker to better target certain files and evade security tools, according to the researchers' report. BlackBerry researchers no...
Source: bankinfosecurity.com