Lazarus Group Exploits Critical Zoho ManageEngine Flaw to Deploy Stealthy QuiteRAT Malware
Lazarus Group, linked to North Korea, exploits Zoho security flaw to spread QuiteRAT trojan.
Source: thehackernews.com
Stay updated with breaking news from Ansomware Malware. Get real-time updates on events, politics, business, and more. Visit us for reliable news and exclusive interviews.
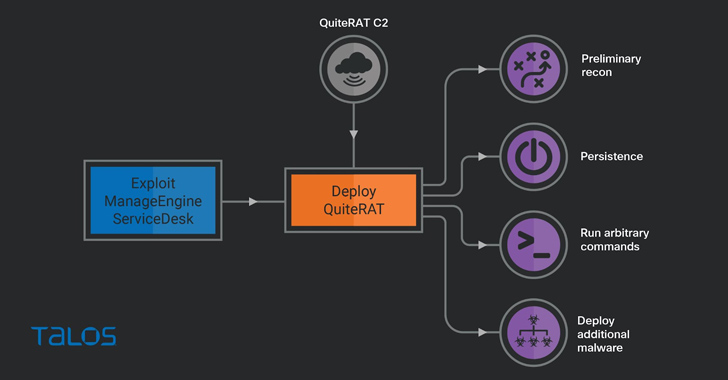
Lazarus Group, linked to North Korea, exploits Zoho security flaw to spread QuiteRAT trojan.
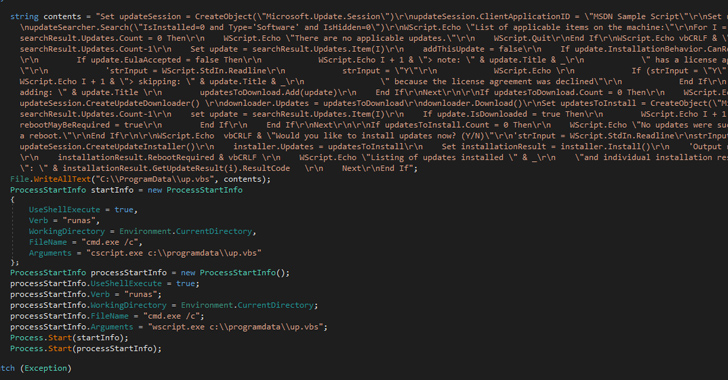
🛡️ Beware of Spacecolon! This malicious tool is spreading Scarab ransomware globally.
FBI alerts of a potential cash out by North Korean actors, linked to $40M in stolen cryptocurrency. This group is currently holding 1,580 bitcoins
#HiatusRAT malware creators return, targeting Taiwan-based orgs & U.S. military procurement system.
New WoofLocker sophisticated toolkit tricks users with fake tech support scams, leveraging advanced fingerprinting and redirection mechanisms.