Critical RCE 0day in Apache Log4j library exploited in the wild (CVE-2021-44228)
A critical zero-day vulnerability in Apache Log4j (CVE-2021-44228), a widely used Java logging library, is being leveraged by attackers.
Source: helpnetsecurity.com
Stay updated with breaking news from Apache Struts. Get real-time updates on events, politics, business, and more. Visit us for reliable news and exclusive interviews.

A critical zero-day vulnerability in Apache Log4j (CVE-2021-44228), a widely used Java logging library, is being leveraged by attackers.
How can orgs get the most from cloud-native environments and agile delivery?
Even the smallest unknown or unpatched vulnerability can be catastrophic.
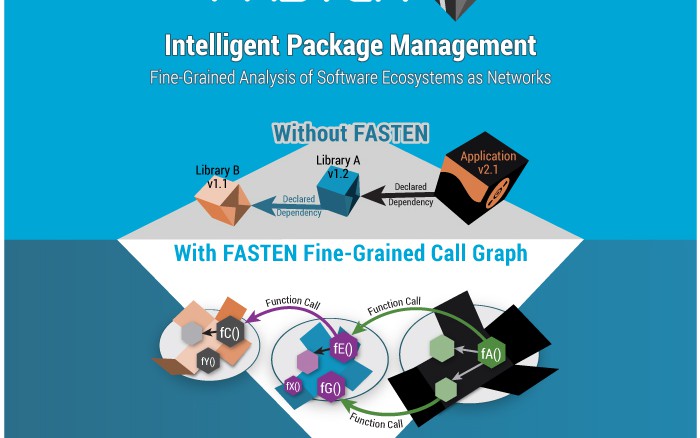
Solving Modern Software Dependency Management Issues This article discusses how build tools such as Maven, Pip, etc. can give more accurate results using call graphs covering both application and its dependencies. by Join the DZone community and get the full member experience.Join For Free In order to help developers tracking dependencies, FASTEN provides a new intelligent package management framework, on top of existing dependency management tools. The FASTEN European research project wants to support DevOps teams by helping them managing and mastering dependencies, at a finer grain level c...

The massive 2017 Equifax hack was done in part by exploiting a critical (though patched) web server vulnerability in Apache Struts, a common and popular form of open source software to creating Java applications. (Equifax) Cybersecurity startup WhiteSource announced it has raised $75 million in Series D funding, highlighting how tech and security investors are increasingly focusing on the open source software security market. The latest investment of $75 million, drawn mostly from Pitango Growth and existing investors M12, Susquehanna Growth Equity, and 83North, is significantly more than the...