Vimarsana
Biggest News Aggregation in the World

Page 37 - Command Line News Today : Breaking News, Live Updates & Top Stories | Vimarsana

Stay updated with breaking news from Command Line. Get real-time updates on events, politics, business, and more. Visit us for reliable news and exclusive interviews.

Top News In Command Line Today - Breaking & Trending Today

Create Database in MySQL - Vimarsana News

Create Database in MySQL

The article provides a detailed overview of how to create a database in MySQL using different methods and tools (including the Command Line, Workbench, and dbForge Studio for MySQL). For details go to: https://blog.devart.com/creating-a-new-database-in-mysql-tutorial-with-examples.html

Related Topics:
Command LineForge Studio
Advanced Persistent Threat (APT) Attacks & Prevention - Vimarsana News

Advanced Persistent Threat (APT) Attacks & Prevention

APTs are sustained & sophisticated efforts to gain access to an organization's network. Discover APT tools now.

Path Finder 2123 U2B macOS - Vimarsana News

Path Finder 2123 U2B macOS

Path Finder 2123 U2B macOS [center][img]https://i.imgur.com/6SRIyOG.png[/img][/center] [center] [quote] Size: 23.22 MB [/quote] [/center] [b]Description:[/b] Path Finder makes you a master of file management. Take full control over your file system. Save your time: compare and synchronize folders...

Microsoft finally makes bypassing Defender scans harder by changing Exclusions permission - Vimarsana News

Microsoft finally makes bypassing Defender scans harder by changing Exclusions permission

Microsoft has made changes to Windows Defender's Exclusions as the section is no longer visible to users who don't have administrator rights, whereas previously, it was visible to everyone.

Source: neowin.net
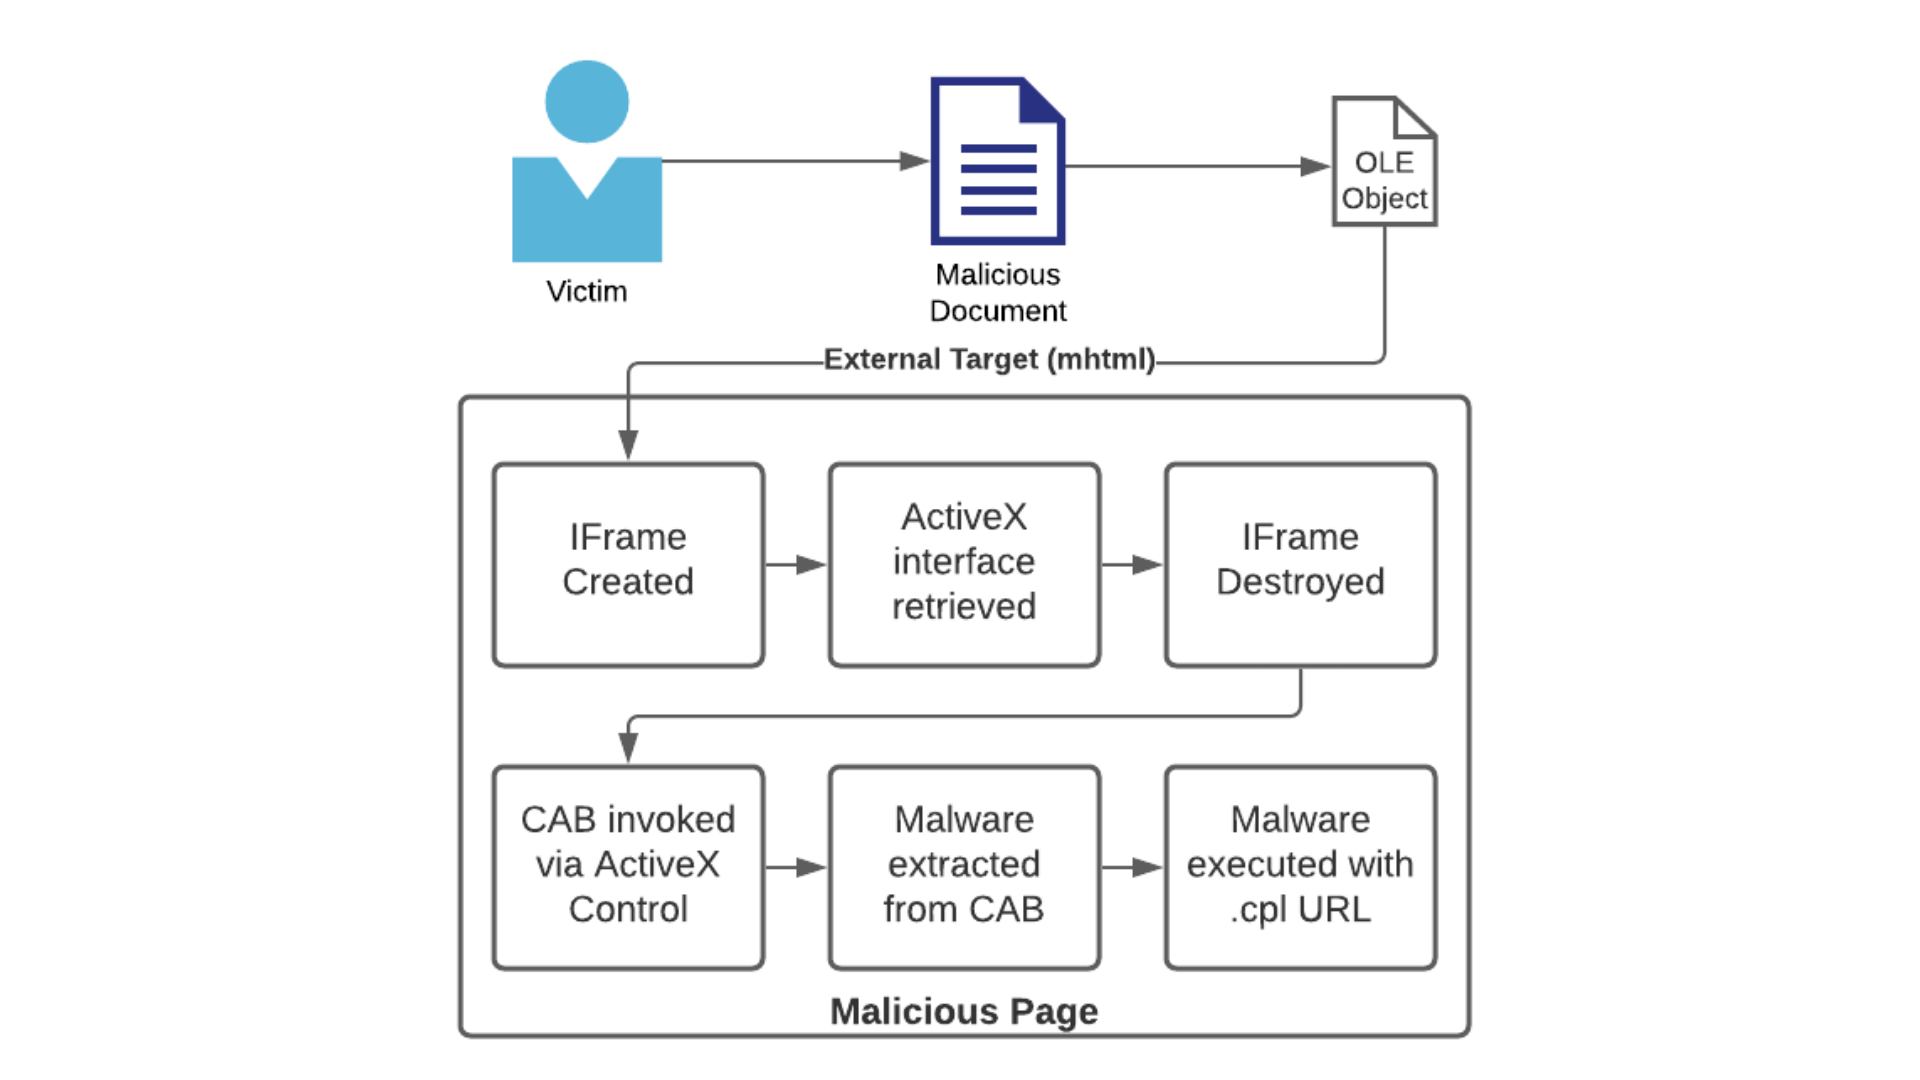
Unpacking CVE-2021-40444: A Deep Technical Analysis of an Office RCE Exploit - Vimarsana News

Unpacking CVE-2021-40444: A Deep Technical Analysis of an Office RCE Exploit

In the middle of August 2021, a special Word document was uploaded to VirusTotal by a user from Argentina. Although it was only detected by a single antivirus engine at the time, this sample turned out to be exploiting a zero day vulnerability in Microsoft Office to gain remote code