Use This One-Click Mitigation Tool from Microsoft to Prevent Exchange Attacks
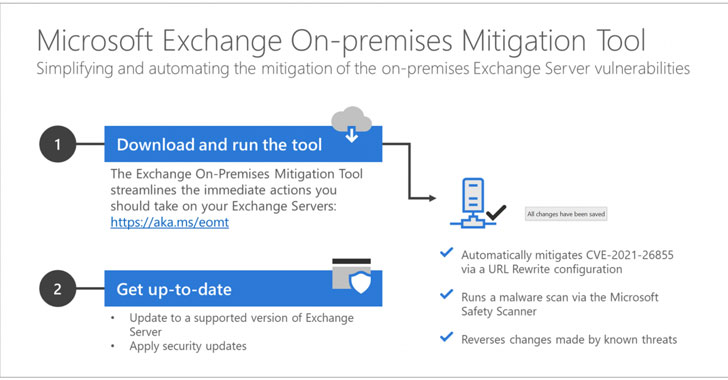
Microsoft released a one-click mitigation software to secure vulnerable environments against the ongoing widespread ProxyLogon Exchange cyberattacks.
Stay updated with breaking news from Cyber Security Updates. Get real-time updates on events, politics, business, and more. Visit us for reliable news and exclusive interviews.
Microsoft released a one-click mitigation software to secure vulnerable environments against the ongoing widespread ProxyLogon Exchange cyberattacks.
CEO of Encrypted Chat Platform Indicted for Aiding Organised Criminals The U.S. Department of Justice (DoJ) on Friday announced an indictment against Jean-Francois Eap, the CEO of encrypted messaging company Sky Global, and an associate for wilfully participating in a criminal enterprise to help international drug traffickers avoid law enforcement. Eap (also known as "888888") and Thomas Herdman, a former high-level distributor of Sky Global devices, have been charged with a conspiracy to violate the federal Racketeer Influenced and Corrupt Organizations Act (RICO), according to warrants issu...
New Browser Attack Allows Tracking Users Online With JavaScript Disabled Researchers have discovered a new side-channel that they say can be reliably exploited to leak information from web browsers that could then be leveraged to track users even when JavaScript is completely disabled. "This is a side-channel attack which doesn't require any JavaScript to run," the researchers said. "This means script blockers cannot stop it. The attacks work even if you strip out all of the fun parts of the web browsing experience. This makes it very difficult to prevent without modifying deep parts of the o...
ProxyLogon PoC Exploit Released; Likely to Fuel More Disruptive Cyber Attacks The U.S. Cybersecurity and Infrastructure Security Agency (CISA) and the Federal Bureau of Investigation (FBI) on Wednesday issued a joint advisory warning of active exploitation of vulnerabilities in Microsoft Exchange on-premises products by nation-state actors and cybercriminals. "CISA and FBI assess that adversaries could exploit these vulnerabilities to compromise networks, steal information, encrypt data for ransom, or even execute a destructive attack," the agencies said. "Adversaries may also sell access to ...
SolarWinds Hack — New Evidence Suggests Potential Links to Chinese Hackers A malicious web shell deployed on Windows systems by leveraging a previously undisclosed zero-day in SolarWinds' Orion network monitoring software may have been the work of a possible Chinese threat group. In a report published by Secureworks on Monday, the cybersecurity firm attributed the intrusions to a threat actor it calls Spiral. Back on December 22, 2020, Microsoft disclosed that a second espionage group may have been abusing the IT infrastructure provider's Orion software to drop a persistent backdoor called ...