TSA formalizes new cybersecurity rules for critical pipeline owners and operators
TSA formalizes new cybersecurity rules for critical pipeline owners and operators - SiliconANGLE
Source: siliconangle.com
Stay updated with breaking news from Daniel Trauner. Get real-time updates on events, politics, business, and more. Visit us for reliable news and exclusive interviews.
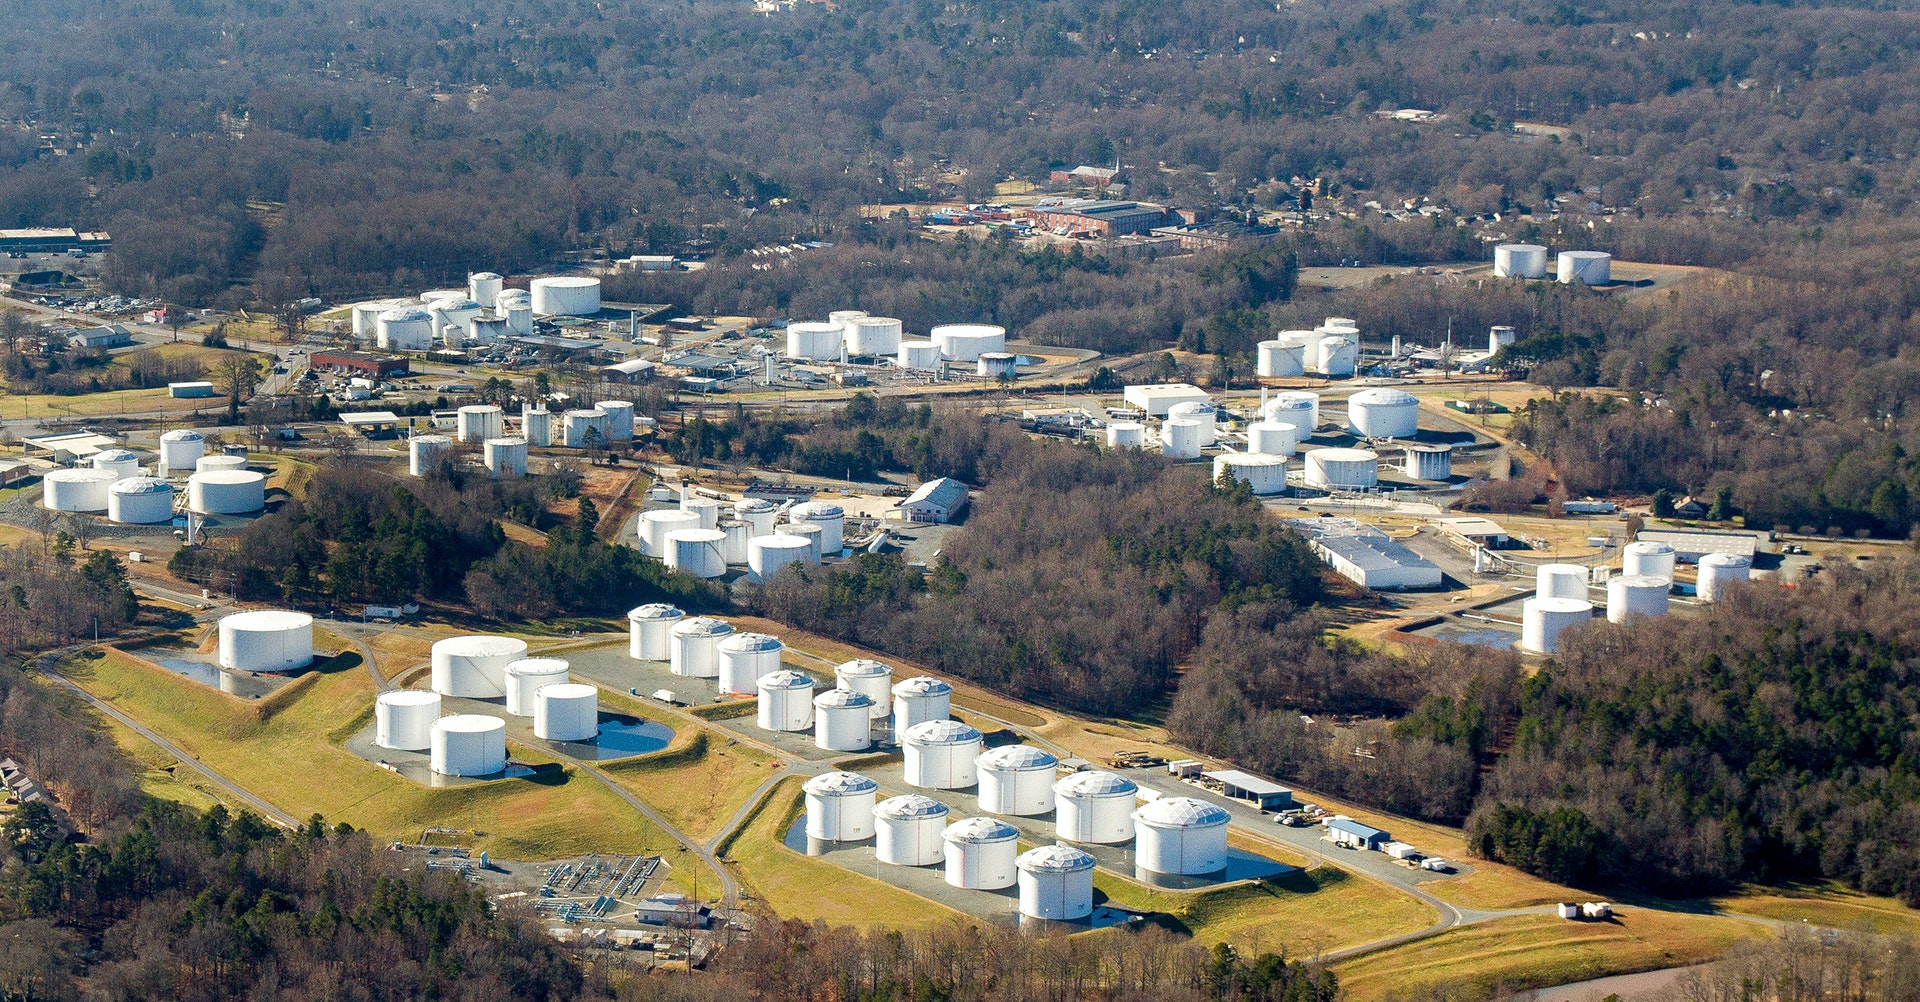
TSA formalizes new cybersecurity rules for critical pipeline owners and operators - SiliconANGLE
SHARE The city of Austin, Texas, is reported to have been hacked and a Russian state-sponsored group is suspected to be behind the intrusion. First reported today by The Intercept, which references documents prepared by the Microsoft Threat Intelligence Center that have not been publicly released, the hack has been traced to mid-October. It’s said to have been used as a jumping-off point for more attacks. The Russian advanced persistent threat group Berserk Bear, which may be linked to Russia’s Federal Security Service, is believed to be behind the attack. Berserk Bear, also known as En...

FireEye on Sunday said that an investigation it was conducting into a breach of its own network last week uncovered a threat actor widely distributing a backdoor dubbed SUNBURST by hiding it in legitimate updates of SolarWinds' Orion network management technology. SUNBURST (SolarWinds.Orion.Core.BusinessLayer dot dll) is a sort of first-stage Trojan that the attackers were using to drop additional payloads for escalating privileges, lateral movement, and data theft on infected networks, FireEye explained. The stealth, planning, and precision with which the attack was executed had all the hal...
Security vendor FireEye uncovered the SolarWinds campaign when investigating a breach of its own network recently that resulted in several of its offensive hacking tools being stolen. As expected, the targeted attack has once again focused attention on the long-standing issue of supply chain and third-party security. It has also raised alarm about the extent to which Russian advanced persistent threat (APT) actors and threat actors from other countries may have insinuated themselves into, and are lurking on, US critical infrastructure and networks, ready to activate at a moment's notice. Broa...
minute read Share this article: Meanwhile, FireEye has found a kill switch, and Microsoft and other vendors are quickly moving to block the Sunburst backdoor used in the attack. SECOND UPDATE A perfect storm may have come together to make SolarWinds such a successful attack vector for the global supply-chain cyberattack discovered this week. Researchers said that includes its use of a default password (“SolarWinds123”) that gave attackers an open door into its software-updating mechanism; and, SolarWinds’ deep visibility into customer networks. Meanwhile, the U.S. Cybers...