Vimarsana
Biggest News Aggregation in the World

Page 3 - Intel Platform News Today : Breaking News, Live Updates & Top Stories | Vimarsana

Stay updated with breaking news from Intel Platform. Get real-time updates on events, politics, business, and more. Visit us for reliable news and exclusive interviews.

Top News In Intel Platform Today - Breaking & Trending Today

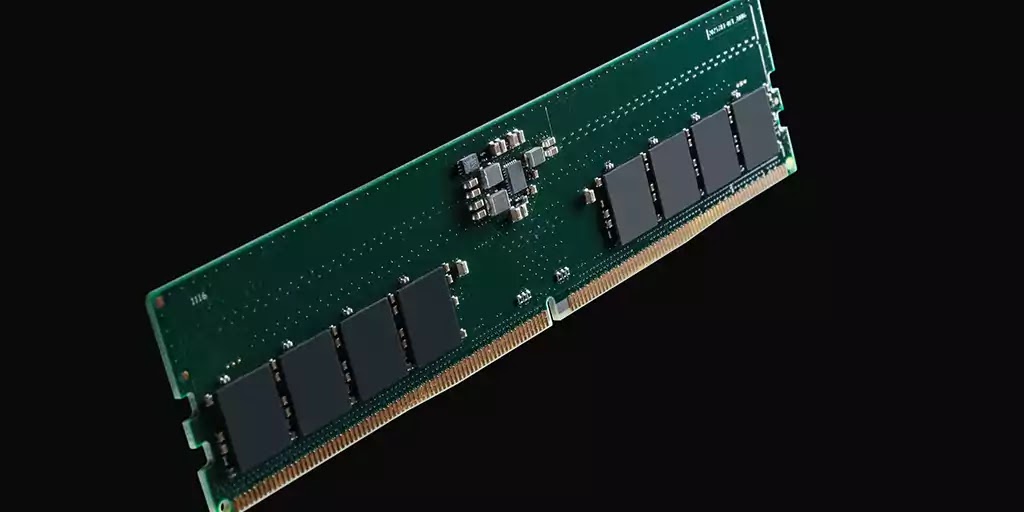
Kingston Technology First Third-Party Supplier to Receive Intel Platform Validation on DDR5 Memory - Vimarsana News

Kingston Technology First Third-Party Supplier to Receive Intel Platform Validation on DDR5 Memory

Kingston Technology, a world leader in memory products and technology solutions, today announced its forthcoming DDR5 UDIMMS has received In...

Kingston Technology First Third-Party Supplier to Receive Intel Platform Validation on DDR5 Memory - Vimarsana News

Kingston Technology First Third-Party Supplier to Receive Intel Platform Validation on DDR5 Memory

FOUNTAIN VALLEY, Calif., Oct. 6, 2021 -- Kingston Technology Company, Inc., a world leader in memory products and technology solutions, today announced

Trusted Platform Module (TPM) im UEFI (BIOS) aktivieren: So geht's - Vimarsana News

Trusted Platform Module (TPM) im UEFI (BIOS) aktivieren: So geht's

10. Juli 2021 um 08:00 Uhr Windows 11 und andere Betriebssysteme lassen sich nur mit einem aktiven Trusted Platform Module (TPM) installieren. So könnt ihr das TPM im BIOS aktivieren. Windows 11, andere Betriebssysteme und Verschlüsselungs- oder Sicherheitssoftware wie BitLocker verlangen einen sogenannten TPM-Chip oder können diesen optional nutzen. Das Kürzel TPM steht für Trusted Platform Module, einem fest im Rechner verbauten Sicherheitschip. In den meisten Windows-Rechnern der letzten Jahre, wie etwa Notebooks, ist ein solches TPM-Modul bereits verbaut. Selbst zusammengebaute Deskt...

Cómo habilitar TPM 2.0 - Vimarsana News

Cómo habilitar TPM 2.0

Cómo habilitar TPM 2.0 Por Javier Gualix - 24/06/2021 21:00 Con Windows 11 recién presentado en sociedad, ahora viene la polémica. En los requisitos mínimos para actualizar al nuevo sistema operativo de Microsoft llegan dos importantes novedades: TPM 2.0 y arranque seguro (Secure Boot, en inglés). Aquí, el problema llega porque muchos equipos no cuentan con estas opciones, principalmente desde 2015 hacia atrás, y en otros más modernos, vienen deshabilitadas. De hecho, es habitual que en los equipos montados a piezas la opción del TPM venga deshabilitada por el fabricante de l...