How to detect the Log4j vulnerability in applications
A bug in the ubiquitous Log4j library can allow an attacker to execute arbitrary code on any system that uses Log4j to write logs.
Source: arnnet.com.au
Stay updated with breaking news from Log4j. Get real-time updates on events, politics, business, and more. Visit us for reliable news and exclusive interviews.

A bug in the ubiquitous Log4j library can allow an attacker to execute arbitrary code on any system that uses Log4j to write logs.

An urgent warning is being issued about the server-software flaw named "Log4Shell." Experts refer to it as one of the most severe computer-security vulnerabilities ever discovered.
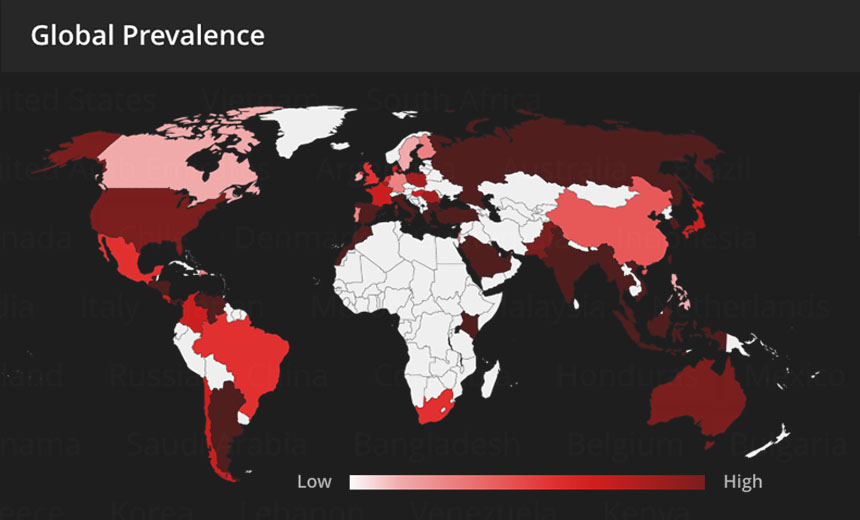
The year is ending with a cybersecurity bang - not whimper - due to the widespread prevalence of the Apache Log4j vulnerability. Researchers warn that at least 40%

The critical vulnerability disclosed last week in Java logging package log4j sent shockwaves throughout the industry given how frequently that open-sour...

Log4Shell, a critical security flaw in Log4j, an open source logging software used in everything from online games to enterprise software and cloud data centres, has security teams all over the world scrambling to fix it. Because of its widespread use, the internet has been put on high alert as hackers increase their efforts to target weak systems. What exactly is the Log4j vulnerability? The vulnerability, also known as Log4Shell, was first discovered by LunaSec researchers.