Exploiting Log4j: 40% of Corporate Networks Targeted So Far
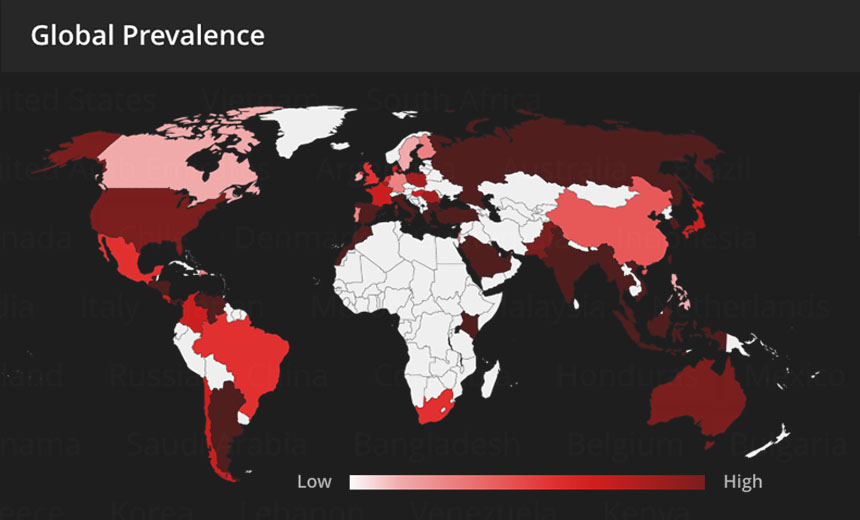
The year is ending with a cybersecurity bang - not whimper - due to the widespread prevalence of the Apache Log4j vulnerability. Researchers warn that at least 40%
Stay updated with breaking news from Log4j. Get real-time updates on events, politics, business, and more. Visit us for reliable news and exclusive interviews.
The year is ending with a cybersecurity bang - not whimper - due to the widespread prevalence of the Apache Log4j vulnerability. Researchers warn that at least 40%
What is Log4j? It is a Java-based logging library developed by the Apache Software Foundation. Log4j is used by a range of services such as Apple iCloud, Minecraft, Amazon, among many others. Here’s what is the vulnerability that everyone is talking about.
A vulnerability in a widely used logging platform uncovered late last week has left security professionals and officials scrambling to respond and patch systems before other nations and cybercriminals can exploit the flaw.
Massive security hole in widely-distributed logging package is a five-alarm fire.
Like CISOs everywhere, Dawn Cappelli of Rockwell Automation awoke last Friday to news about the Log4j vulnerability and the risk it posed to her company, customers