Buer Dropper Malware Updated Using Rust
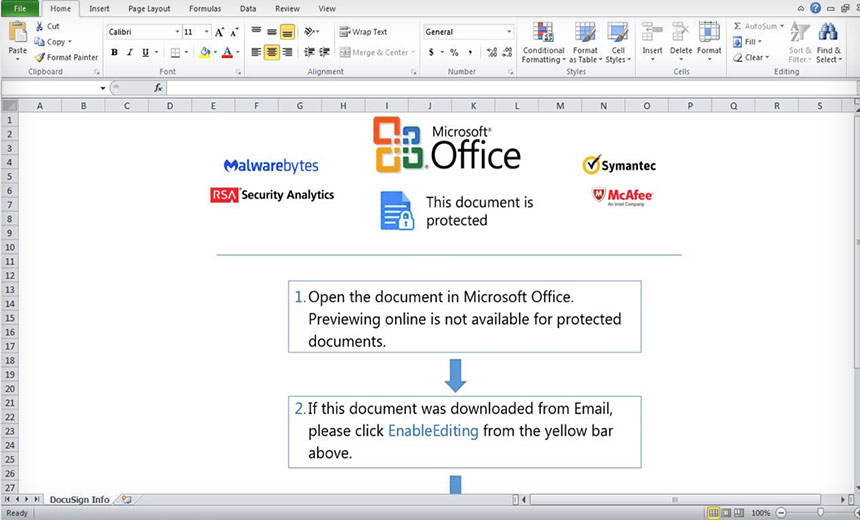
BankInfoSecurity May 20, 2021 Compliance May 4, 2021 Compliance Compliance Compliance DougOlenick) • May 3, 2021 A malicious attachment containing RustyBuer malware (Source: Proofpoint) Attackers are using a freshly updated variant of the Buer first-stage malware loader rewritten in the Rust programming language to help evade detection, the security firm Proofpoint reports. In April, researchers observed the loader, dubbed RustyBuer, being distributed via emails purporting to be DHL shipping support notices. Pr...
Source: bankinfosecurity.com