Vimarsana
Biggest News Aggregation in the World

Page 3 - Password Stores News Today : Breaking News, Live Updates & Top Stories | Vimarsana

Stay updated with breaking news from Password Stores. Get real-time updates on events, politics, business, and more. Visit us for reliable news and exclusive interviews.

Top News In Password Stores Today - Breaking & Trending Today

NSA and CISA Red and Blue Teams Share Top Ten Cybersecurity Misconfigurations - Vimarsana News

NSA and CISA Red and Blue Teams Share Top Ten Cybersecurity Misconfigurations

A plea for network defenders and software manufacturers to fix common problems. EXECUTIVE SUMMARY The National Security Agency (NSA) and Cybersecurity and Infrastructure Security Agency (CISA) are releasing this joint cybersecurity advisory (CSA) to highlight the most common cybersecurity misconfigurations in large organizations, and detail the tactics, techniques, and procedures (TTPs) actors use to exploit

Sponsor with batch-filed whiskers: Ballistic Bobcat's scan and strike backdoor - Vimarsana News

Sponsor with batch-filed whiskers: Ballistic Bobcat's scan and strike backdoor

ESET Research uncovers the Sponsoring Access campaign, which utilizes an undocumented Ballistic Bobcat backdoor we have named Sponsor.

Picus Threat Library Is Updated for Trojans Targeting Banks in Latin America - Vimarsana News

Picus Threat Library Is Updated for Trojans Targeting Banks in Latin America

Picus Labs has updated the Picus Threat Library with new attack methods for Krachulka, Lokorrito, Zumanek Trojans that are targeting banks in Brazil, Mexico, and Spain. In this blog, techniques used by these malware families will be explored. Banking trojans have a significant role in the cybercrime scene in Latin America. According to Eset, 11 different malware families that target banks in Spanish and Portuguese-speaking countries share TTPs, indicating that threat actors are cooperating on some level. For example, the same or similar custom encryption schemes are used by these malware famil...

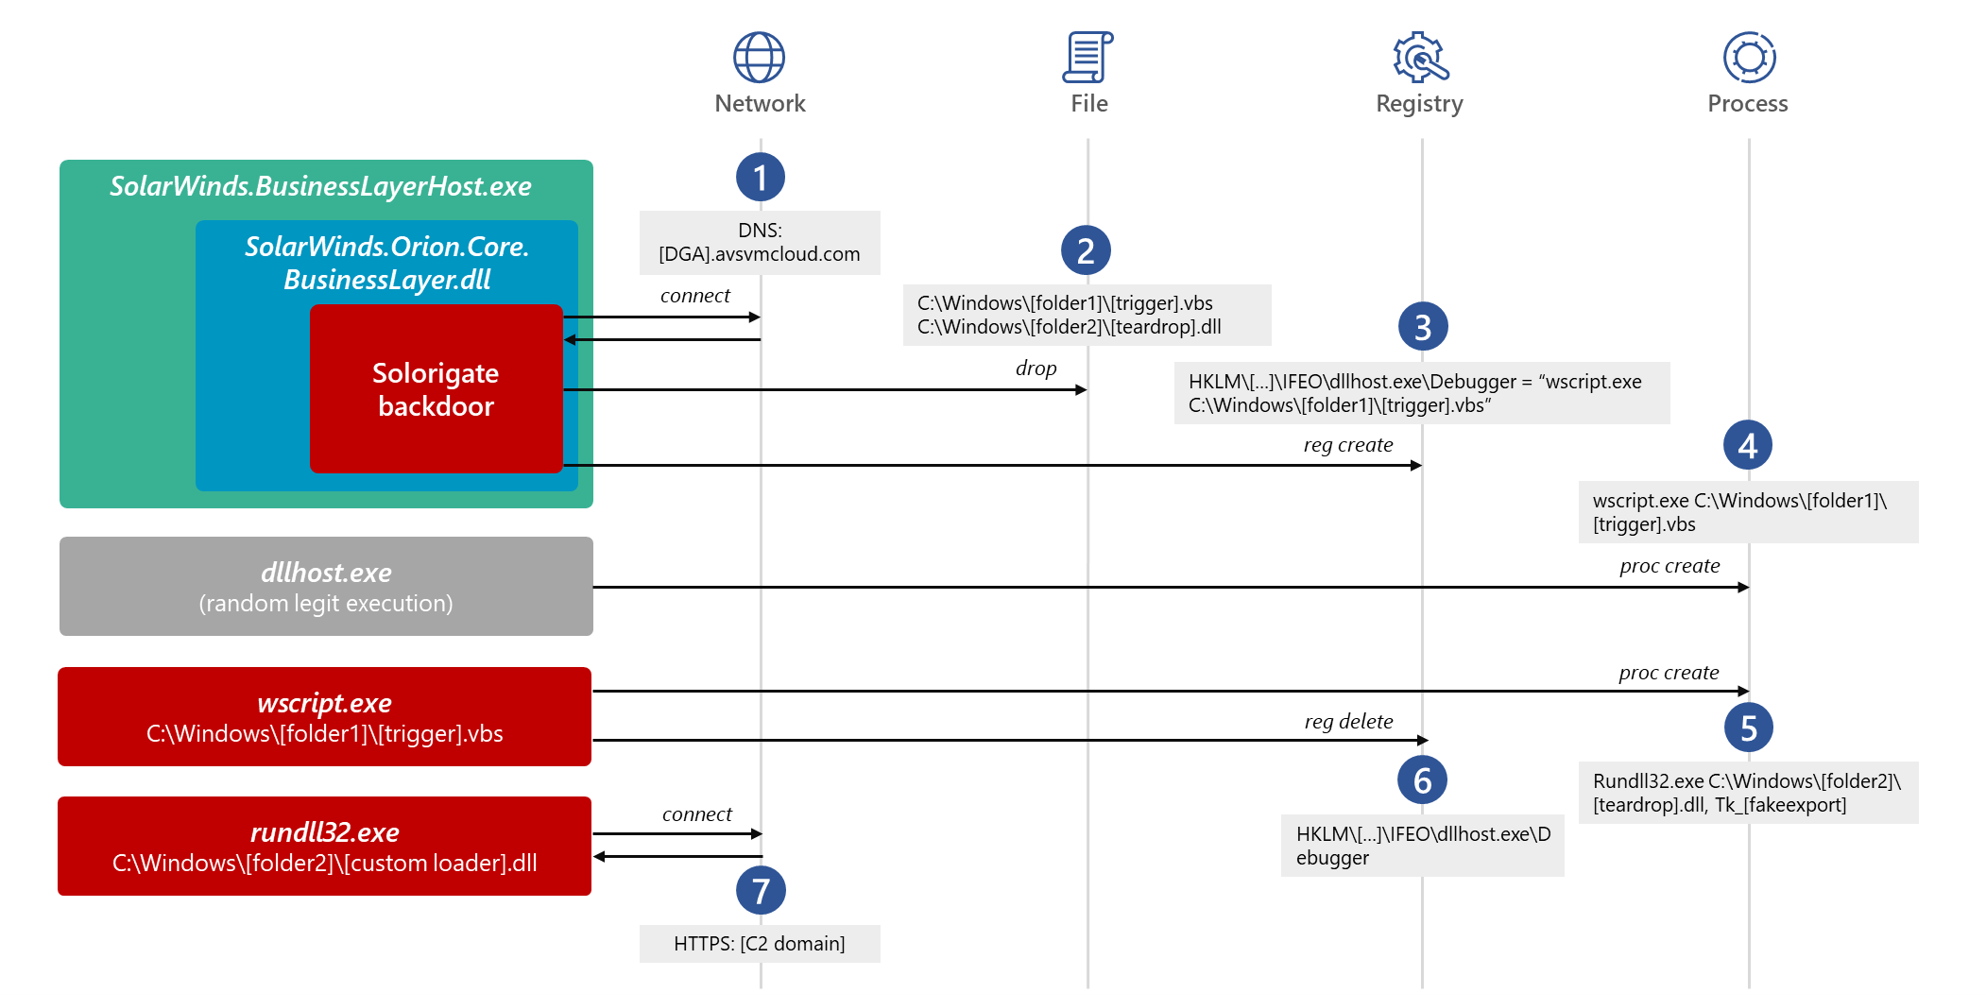
Deep dive into the Solorigate second-stage activation: From SUNBURST to TEARDROP and Raindrop - Vimarsana News

Deep dive into the Solorigate second-stage activation: From SUNBURST to TEARDROP and Raindrop

UPDATE: Microsoft continues to work with partners and customers to expand our knowledge of the threat actor behind the nation-state cyberattacks that compromised the supply chain of SolarWinds and impacted multiple other organizations. Microsoft previously used ‘Solorigate’ as the primary designation for the actor, but moving forward, we want to place appropriate focus on the actors behind the sophisticated attacks, rather than one of the examples of malware used by the actors. Microsoft Threat Intelligence Center (MSTIC) has named the actor behind the attack against SolarWinds, the SUNBU...