Hacking the US Government -- Legally
Most federal executive branch agencies in the U.S. now have vulnerability disclosure policies. John Jackson and Jackson Henry of the security research group Sakura
Source: govinfosecurity.com
Stay updated with breaking news from Vulnerability Disclosure Programs. Get real-time updates on events, politics, business, and more. Visit us for reliable news and exclusive interviews.
Most federal executive branch agencies in the U.S. now have vulnerability disclosure policies. John Jackson and Jackson Henry of the security research group Sakura
Reporting security vulnerabilities to organizations with no disclosure policies can be fraught with tension. In the worst conflicts, security researchers could face
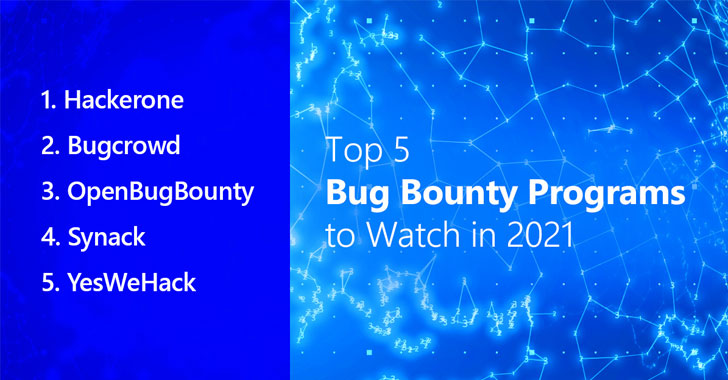
Top 5 Bug Bounty Platforms to Watch in 2021 While Gartner does not have a dedicated Magic Quadrant for Bug Bounties or Crowd Security Testing yet, Gartner Peer Insights already lists 24 vendors in the "Application Crowdtesting Services" category. We have compiled the top 5 most promising bug bounty platforms for those of you who are looking to enhance your existing software testing arsenal with knowledge and expertise from international security researchers: 1. HackerOne Being a unicorn backed by numerous reputable venture capitalists, HackerOne is probably the most well-known and recognized...

Several U.S. government networks, including the Treasury, Commerce and Homeland Security Departments, have each been hit by a major cyberespionage campaign operated by Russian hackers. The list of victims of the cyberattack is expected to expand as more information comes to light Given that the agency set-up to safeguard the U.S. from cyber and physical threats was also breached highlights how any government agency is at risk from state-sponsored threats. With the attack, the hackers were apparently able to access internal emails sent by the US Treasury and Commerce Department. The hackers ...

Some of your friends information with you. you're only bringing your own and you're able to connect with friends who have authorized it directly. >> let me turn to the bug bounty program. our subcommittee has had a hearing. your press release indicated that was one of the six changes facebook initially offered to crack down on abuses. rewarding outside parties who find vulnerabilities. one concern i have regarding the utility of this approach is the vulnerability disclosure programs are normally geared toward identifying unauthorized access to data. not pointing out data sharing arrangements t...