Operation ChattyGoblin: Hackers Targeting Gambling Firms via Chat Apps
A China-aligned threat actor has been targeting gambling companies in Southeast Asia since October 2021.
Source: thehackernews.com
Stay updated with breaking news from Yber Updates. Get real-time updates on events, politics, business, and more. Visit us for reliable news and exclusive interviews.
A China-aligned threat actor has been targeting gambling companies in Southeast Asia since October 2021.
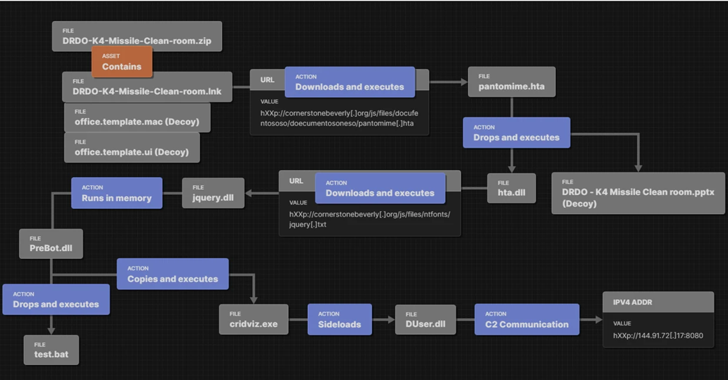
Action RAT and AllaKore RAT are the latest strains of malware deployed by SideCopy to carry out spear-phishing email attacks using Indian government.
North Korean hackers Kimsuky using new ReconShark reconnaissance tool to target individuals via spear-phishing.
East Asian markets hit by a new Android malware named FluHorse.
Meta reveals the takedown of fraudulent news media brands, hacktivist groups, and NGOs engaged in coordinated inauthentic behavior.