Forrester Expert Explores Latest Supply Chain Attack Trends
Supply chain attacks have evolved from exploiting organizations with unpatched vulnerabilities in open-source libraries to proactively injecting malicious code into
Stay updated with breaking news from Dependency Confusion. Get real-time updates on events, politics, business, and more. Visit us for reliable news and exclusive interviews.
Supply chain attacks have evolved from exploiting organizations with unpatched vulnerabilities in open-source libraries to proactively injecting malicious code into
Software supply chain security helps protect all components, processes, and activities related to building and deploying software.
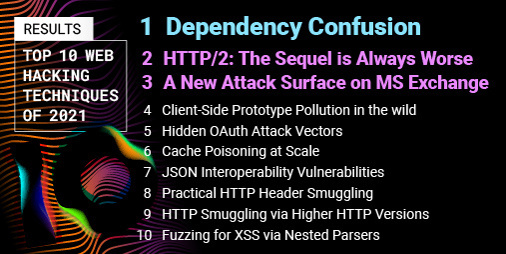
Welcome to the Top 10 (new) Web Hacking Techniques of 2021, the latest iteration of our annual community-powered effort to identify the most significant web security research released in the last year
Malicious NPM packages target Amazon, Slack with new dependency attacks By 12:14 AM Threat actors are targeting Amazon, Zillow, Lyft, and Slack NodeJS apps using a new 'Dependency Confusion' vulnerability to steal Linux/Unix password files and open reverse shells back to the attackers. Last month, BleepingComputer reported that security researcher Alex Birsan earned bug bounties from 35 companies by utilizing a new flaw in open-source development tools. This flaw works by attackers creating packages utilizing the same names as a company's internal repositories or components. When hosted on...