Chinese Hackers Target Semiconductor Firms in East Asia with Cobalt Strike
Semiconductor companies in East Asia are under attack. Threat actors posing as TSMC deploy Cobalt Strike beacons via HyperBro backdoor
Source: thehackernews.com
Stay updated with breaking news from Lucky Mouse. Get real-time updates on events, politics, business, and more. Visit us for reliable news and exclusive interviews.
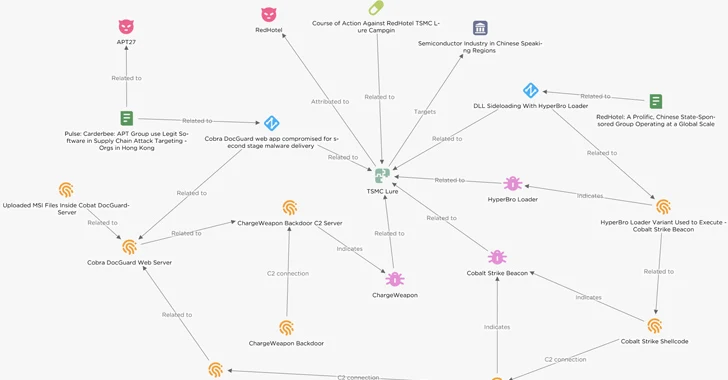
Semiconductor companies in East Asia are under attack. Threat actors posing as TSMC deploy Cobalt Strike beacons via HyperBro backdoor

New attacks with the updated SysUpdate toolkit have been deployed by Chinese advanced persistent threat operation Budworm, also known as APT27, Emissary Panda, Bronze Union, Lucky Mouse, Iron Tiger, and Red Phoenix, against an Asian government and a Middle East-based telecommunications provider, reports The Hacker News.

Bootkit can compromise Windows 11, a hacked container found and more. Welcome to Cyber Security Today. It's Friday, March 3rd, 2023. I'm Howard Solomon, contributing reporter on cybersecurity for ITWorldCanada.com and TechNewsday.com in the U.S. A bootkit being sold to crooks can bypass and corrupt a fully-patched Windows 11 system, say researchers at ESET. Called
Budworm APT group of hackers has resurfaced after 6 years with new cyber espionage attacks targeted at U.S. organizations.
China-linked cyberespionage group APT27 was recently observed targeting a US state legislature.