Vimarsana
Biggest News Aggregation in the World

Page 6 - Microsoft Installer News Today : Breaking News, Live Updates & Top Stories | Vimarsana

Stay updated with breaking news from Microsoft Installer. Get real-time updates on events, politics, business, and more. Visit us for reliable news and exclusive interviews.

Top News In Microsoft Installer Today - Breaking & Trending Today

Bizarro banking Trojan goes global - Vimarsana News

Bizarro banking Trojan goes global

May 18, 2021 Kaspersky researchers have discovered a new banking malware from Brazil, named Bizarro, targeting 70 banks from different European and South American countries. Last year, Kaspersky researchers saw several banking trojans from South America (Guildma, Javali, Melcoz and Grandoreiro), expanding their operations all over the globe. Collectively recognised as “the Tétrade”, these families employed a variety of new, innovative and sophisticated techniques. 2021 has seen a continuation of this trend as a new local player, Bizarro, goes global. Bizarro is a new banking Trojan famil...

Bizarro Banking Trojan Sports Sophisticated Backdoor - Vimarsana News

Bizarro Banking Trojan Sports Sophisticated Backdoor

The advanced Brazilian malware has gone global, harvesting bank logins from Android mobile users. A never-before-documented Brazilian banking trojan, dubbed Bizarro, is targeting customers of 70 banks scattered throughout Europe and South America, researchers said. According to an analysis from Kaspersky released Monday, Bizarro is a mobile malware, aimed at capturing online-banking credentials and hijacking Bitcoin wallets from Android users. It spreads via Microsoft Installer packages, which are either downloaded directly by victims from links in spam emails or installed via a trojanized ap...

'MountLocker' Ransomware Adds to Affiliate Extortion Racket - Vimarsana News

'MountLocker' Ransomware Adds to Affiliate Extortion Racket

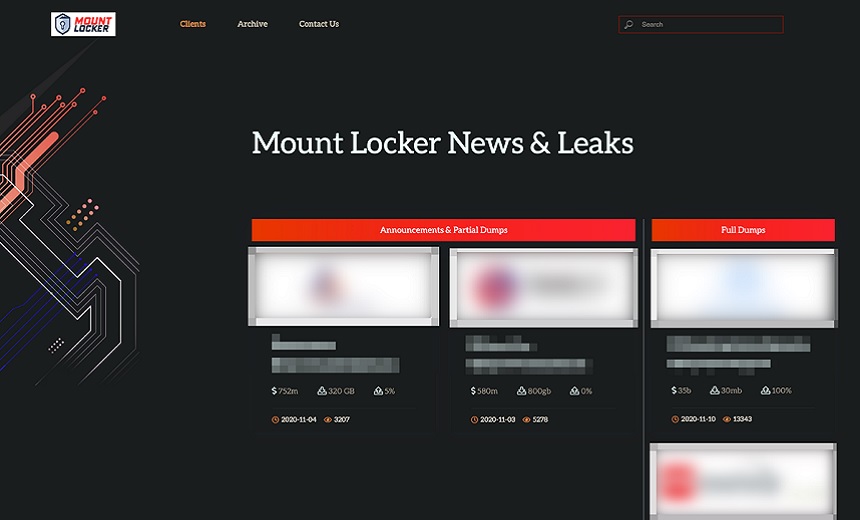
MountLocker's "News & Leaks" site hosted on the darknet (Source: BlackBerry) BlackBerry researchers are tracking a relatively new ransomware variant called MountLocker and the operators behind it, who are using affiliate cybercriminal gangs to help spread the malware, exfiltrate data and extort victims, sometimes for millions of dollars. The ransomware was first spotted by BlackBerry's Incident Response Team in July, and its code was updated in November to allow MountLocker to better target certain files and evade security tools, according to the researchers' report. BlackBerry researchers no...