Colonial Pipeline Hack and Havoc
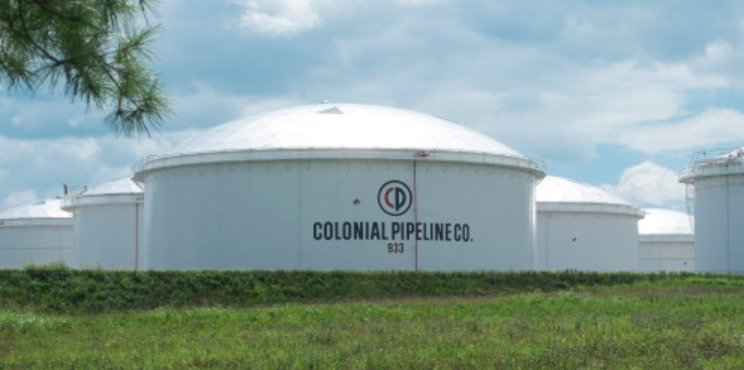
A ransomware attack shut down the U..S. Colonial Pipeline The FBI confirms that the Darkside ransomware is responsible for the compromise of the Colonial Pipeline networks. We continue to work with the company and our government partners on the investigation. Reports are that the Pipeline paid a $5 M ransom. We will update. Official Releases On May 7, the Colonial Pipeline Company learned it was the victim of a cybersecurity attack. We have since determined that this incident involves ransomware. In response, we proactively took certain systems offline to contain the threat, which has te...
Source: sofmag.com