Mustang Panda Targets Asia with Advanced PlugX Variant DOPLUGS
Mustang Panda escalates cyber espionage in Asia with advanced DOPLUGS malware. Discover how this China-linked group targets nations with sophisticated
Source: thehackernews.com
Stay updated with breaking news from Red Lich. Get real-time updates on events, politics, business, and more. Visit us for reliable news and exclusive interviews.
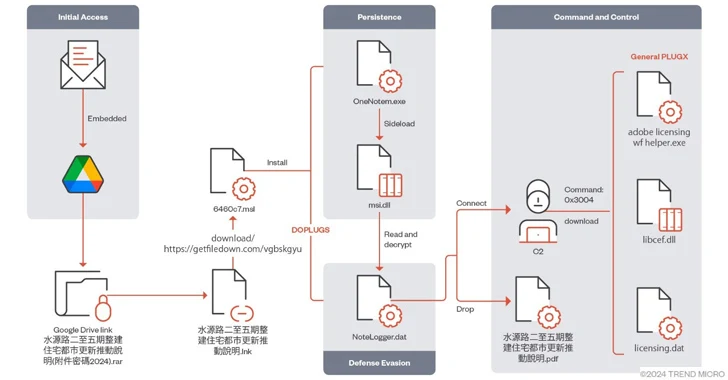
Mustang Panda escalates cyber espionage in Asia with advanced DOPLUGS malware. Discover how this China-linked group targets nations with sophisticated

Chinese state-sponsored advanced persistent threat group Mustang Panda, also known as Earth Preta, Bronze President, Camaro Dragon, HoneyMyte, RedDelta, BASIN, and Red Lich, has launched new attacks exploiting TP-Link routers to compromise European foreign affairs organizations since January, according to The Hacker News.
Chinese state-sponsored advanced persistent threat operation Mustang Panda, also known as Earth Preta, RedDelta, Bronze President, Red Lich, and HoneyMyte, has strengthened its techniques for evading the detection of security solutions, The Hacker News reports.
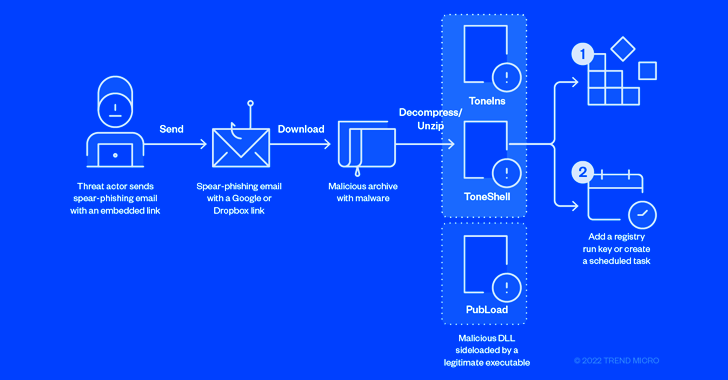
Chinese Mustang Panda hackers have been linked to a spate of spear-phishing attacks targeting governments, educational institutions, and researchers.
Hackers from China used the PlugX malware to attack government officials in Europe, the Middle East, and South America.