Ransomware Operators Using SystemBC Malware as Backdoor
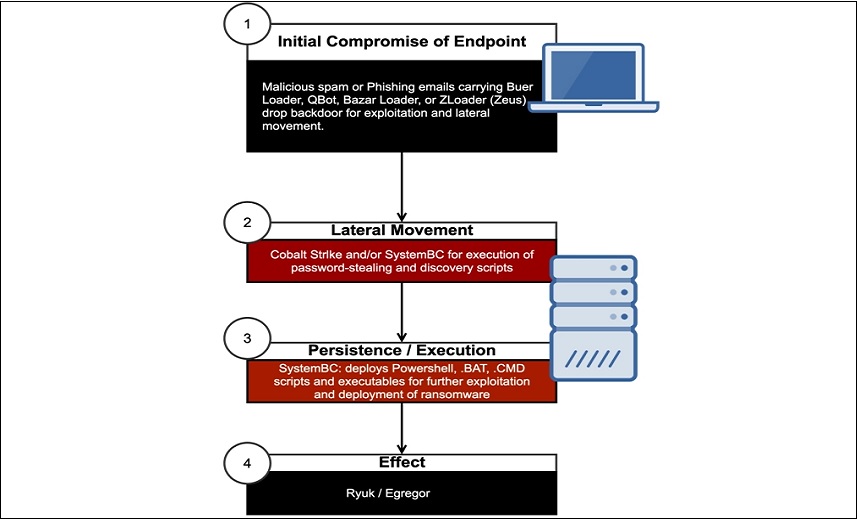
Diagram shows how ransomware operators incorporate the SystemBC malware into an attack. (Source: Sophos) Several recent ransomware attacks, including those involving Ryuk and Egregor, have used a commodity malware variant called SystemBC as a backdoor, security firm Sophos reports. First uncovered by security firm Proofpoint in August 2019, SystemBC works as a network proxy for concealed communications and as a remote access Trojan, or RAT, that allows threat actors to deploy additional commands and scripts to infected Windows devices and to gather data. While researchers have tracked SystemB...
Source: bankinfosecurity.com
