Fodcha DDoS Botnet Resurfaces with New Capabilities
The threat actor behind the Fodcha distributed denial-of-service (DDoS) botnet has resurfaced with new capabilities, researchers reveal.
Source: thehackernews.com
Stay updated with breaking news from Network Security Research Lab. Get real-time updates on events, politics, business, and more. Visit us for reliable news and exclusive interviews.
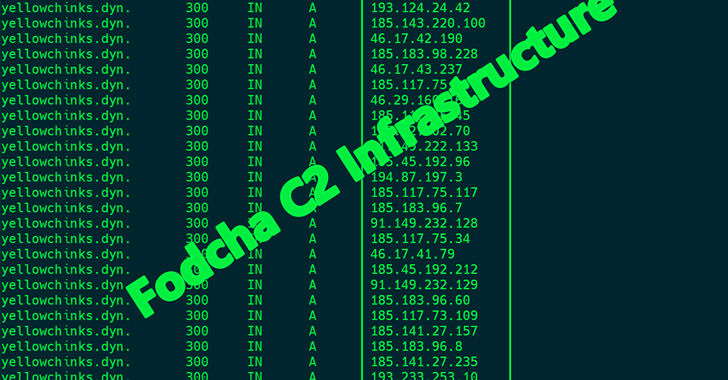
The threat actor behind the Fodcha distributed denial-of-service (DDoS) botnet has resurfaced with new capabilities, researchers reveal.
Major security bugs are a long-term threat: Here's why and what's next - SiliconANGLE
A recently discovered botnet is infecting thousands of AT&T internet subscribers in the U.S., using a critical-severity blind command injection flaw first reported
A recently discovered botnet is infecting thousands of AT&T internet subscribers in the U.S., using a critical-severity blind command injection flaw first reported

10 March 2021, 3:23 am EST By Crypto mining malware continue their attack on the Network-Attached Storage (NAS) NAS are products of QNAP, a popular Taiwanese storage manufacturer. It is similar to an external storage device that can be expandable up to 16 Terabytes. The researchers first discovered the malware at Qihoo 360's Network Security Research Lab (360 Netlab). The attack happens in two segments. The attacker gains control of the QNAP device and runs arbitrary commands. 360 Netlab reports on March 2, 2021, about attacks through the QNAP NAS devices via unauthorized remote command exec...