CISA Directs Federal Agencies to Patch Known Vulnerabilities
The U.S. Cybersecurity and Infrastructure Security Agency on Wednesday issued a new directive - BOD 22-01 - requiring federal civilian agencies to patch
Source: govinfosecurity.com
Stay updated with breaking news from Programs Directorate. Get real-time updates on events, politics, business, and more. Visit us for reliable news and exclusive interviews.
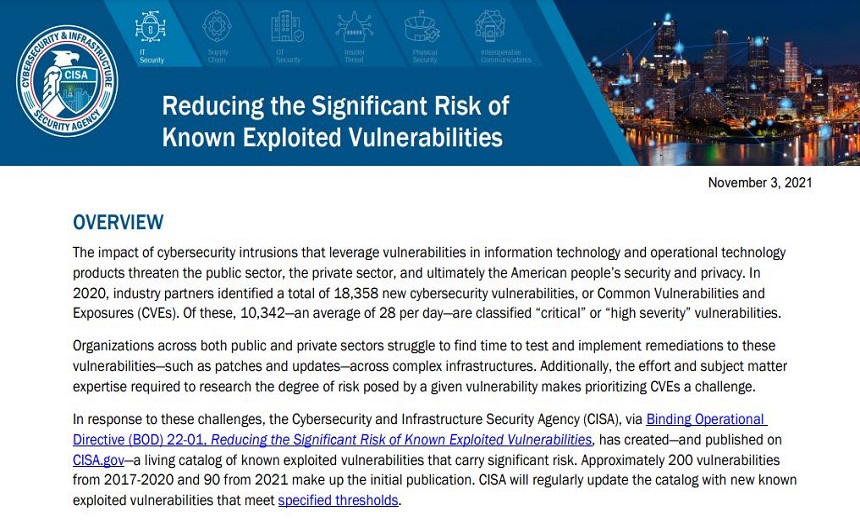
The U.S. Cybersecurity and Infrastructure Security Agency on Wednesday issued a new directive - BOD 22-01 - requiring federal civilian agencies to patch
The U.S. Cybersecurity and Infrastructure Security Agency on Wednesday issued a new directive - BOD 22-01 - requiring federal civilian agencies to patch

Krebs spent 2020 working furiously to ensure the integrity of our elections, while also ensuring that ransomware, software supply-chain vulnerabilities and a range of other rapidly escalating risks didn't cripple government operations or the nation's critical infrastructure.
Matt Hartman, the deputy executive assistant director for cyber at CISA, said without EINSTEIN, there may be departments today that still did not know they were…
By Aleksandr Yampolskiy, Philip Reitinger May 10, 2021 Every time there’s another massive cybersecurity breach, which like SolarWinds finds its roots in a security issue at a third party, policymakers and security experts ask, “Where do we go from here?” The private sector and the federal government haven’t figured out how agencies can best address risks posed by their vendors. The problem is especially acute for small- and mid-sized organizations. Individually engaging, evaluating and auditing every vendor, from custodial services to cloud providers, is cost prohibitive and unreali...