Ransomware Gang Exploits Old Fortinet VPN Flaw
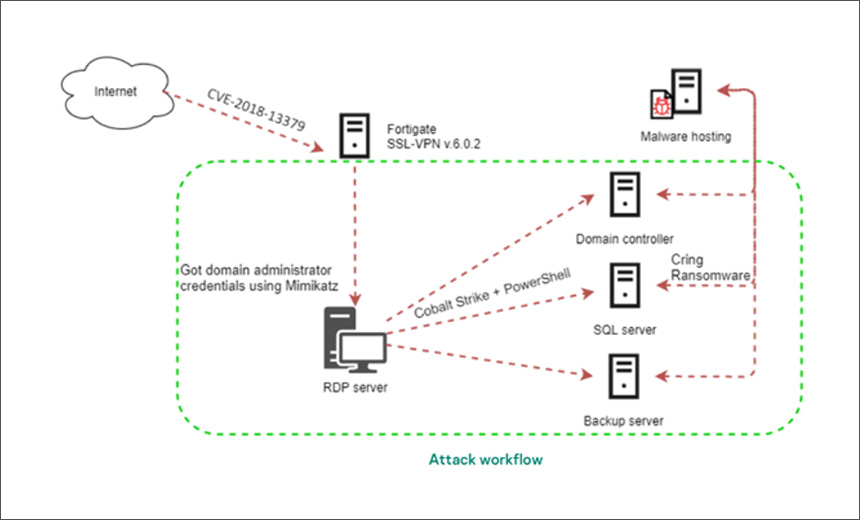
The attack workflow starts by exploiting an old Fortigate VPN server flaw. (Source: Kaspersky) The gang behind ransomware dubbed "Cring," which has waged a series of attacks this year, is exploiting a Fortinet VPN server vulnerability that the company patched in 2019, according to a report from the security firm Kaspersky that analyzes one attack in Europe. The researchers report that the ongoing campaign, which began in January, exploits the Fortigate VPN server flaw tracked as CVE-2018-13379 to gain initial access. Once in the victim's environment, the attackers encrypt data and then demand...
Source: databreachtoday.com
