4 steps to protect the C-suite from business email compromise attacks
Preventing top executives from becoming BEC victims requires a different approach. Putting the risk in business terms is key.
Source: csoonline.com
Stay updated with breaking news from Hold Security. Get real-time updates on events, politics, business, and more. Visit us for reliable news and exclusive interviews.
Preventing top executives from becoming BEC victims requires a different approach. Putting the risk in business terms is key.
share Print A Russian-based hacker group blamed for a massive ransomware attack earlier this month has gone offline, sparking speculation about whether the move was the result of a government-led action. The webpages of the group known as REvil disappeared from the dark web on July 13, cybersecurity researchers said. Both its data-leak site and ransom-negotiating portals were unreachable. The researchers said that it was unclear whether the outage was the result of actions taken by law enforcement or whether REvil had voluntarily taken down its sites. "The situation is still unfolding, but ev...
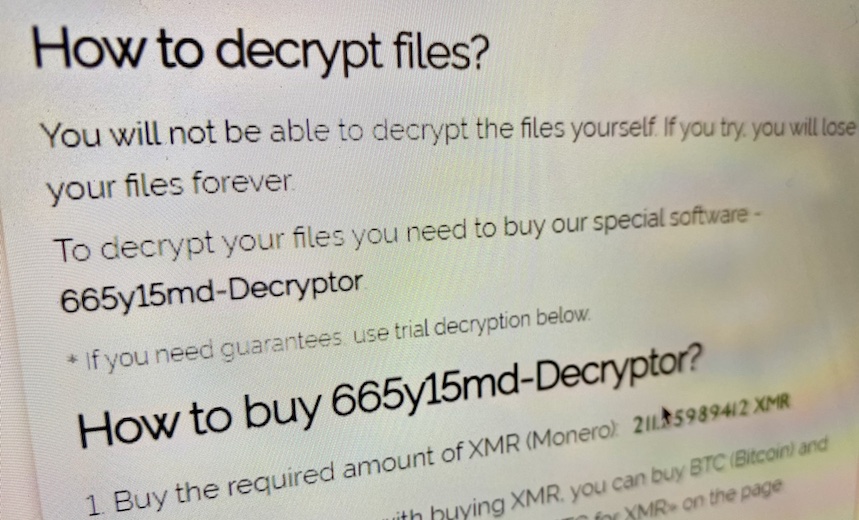
A screenshot of a negotiating portal set up by the REvil ransomware group (Source: SecurityScorecard) Threat intelligence researchers are looking closely at REvil, the ransomware gang that infected up to 1,500 companies in a single swoop. A look at part of the group's online infrastructure shows clear lines to Russian and U.K. service providers that, in theory, could help law enforcement agencies but don't appear eager to help. On July 2, affiliates of REvil exploited several vulnerabilities in remote management software called the Virtual System Administrator from Miami-based Kaseya. The U...

6-year-old Kaseya vulnerability surfaces amid VSA supply chain attack Allowed users to read server files containing usernames, passwords and the location of key databases. Credit: 217194570 © Transversospinales | Dreamstime.com A six-year-old flaw lying in Kaseya’s deprecated billing and customer support site has surfaced amid the ongoing attempt to rectify a supply chain attack on the vendor's VSA product that has affected over 1000 businesses globally. Last week, the US-based IT infrastructure management solutions vendor discovered a potential security incident involving ...

Some 26 million passwords were exposed in a 1.2 terabyte batch of data found by NordLocker, a security company. It's workaday botnet data, but it highlights a hostile malware landscape, particularly for people still inclined to download pirated software.