Vimarsana
Biggest News Aggregation in the World

Page 3 - Software Link News Today : Breaking News, Live Updates & Top Stories | Vimarsana

Stay updated with breaking news from Software Link. Get real-time updates on events, politics, business, and more. Visit us for reliable news and exclusive interviews.

Top News In Software Link Today - Breaking & Trending Today

WPSG Eyewitness News On The CW Philly September 4, 2014 - Vimarsana News

WPSG Eyewitness News On The CW Philly September 4, 2014

Away on roselyn street earlier in the day. No victim was found when shooting was reported there at 4 00p m but eyewitnesses described seeing that same car. They interviewed several witness that he is say a male was shot sitting in the passenger seat on the miss bush i. Driver then sped away. At this point no arrests have been made, heavy set man was seen running from the burning car, but it is unclear how or if he is involved. It is also unclear who may have vote victim as he is indeed the same man who was found burned beyond recognition. We cannot tell at this time if he is shot. Of course no...

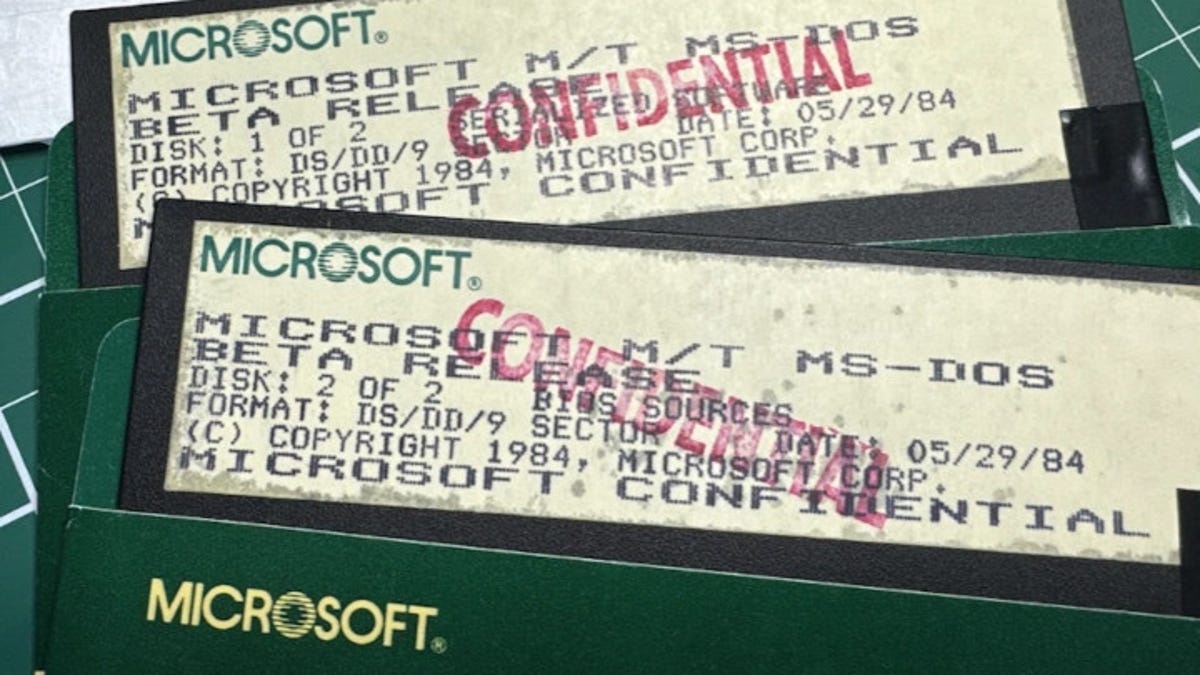
It's baaack! Microsoft and IBM open source MS-DOS 4.0 - Vimarsana News

It's baaack! Microsoft and IBM open source MS-DOS 4.0

How did the operating system so bad it likely steered users to Linux 35 years ago come to be open-sourced now? Here's what happened.

Source: zdnet.com
(Almost) Every infrastructure decision I endorse or regret after 4 years running infrastructure at a startup - Vimarsana News

(Almost) Every infrastructure decision I endorse or regret after 4 years running infrastructure at a startup

Assortment of technology startup infrastructure recommendations

Source: cep.dev
ChurchCRM 4.5.4 SQL Injection - KizzMyAnthia.com - Vimarsana News

ChurchCRM 4.5.4 SQL Injection - KizzMyAnthia.com

# Exploit Title: ChurchCRM 4.5.4 - Authenticated Blind SQL Injection via the EN_tyid# Date: 03-05-2023# Exploit Author: Arvandy# Blog Post: https://github.com/arvandy/CVE/blob/main/CVE-2023-29842/CVE-2023-29842.md# Software Link: https://github.com/ChurchCRM/CRM/releases# Vendor Homepage: http://churchcrm.io/# Version: 4.5.4# Tested on: Windows, Linux# CVE: CVE-2023-29842"""The endpoint /EditEventTypes.php is vulnerable to Blind SQL Injection (Time-based) via the EN_tyid POST parameter.This endpoint can be triggered through the

WordPress WP ERP 1.12.2 SQL Injection - KizzMyAnthia.com - Vimarsana News

WordPress WP ERP 1.12.2 SQL Injection - KizzMyAnthia.com

# Exploit Title: WP Plugins WP ERP